Option A · one-time
Emergency hack cleanup
For sites that are hacked, redirected, or blacklisted.
- Deep scan of files and the database
- Manual malware and backdoor removal
- Search-engine re-index support
WordPress Security Services
Over 90% of WordPress threats hit third-party plugins and themes — not core. Secure the store or business site against malware, bots, and data leaks before they cost revenue.
Urgency
Scanners do not wait for your Monday update window. Neither should the people who lock the site.
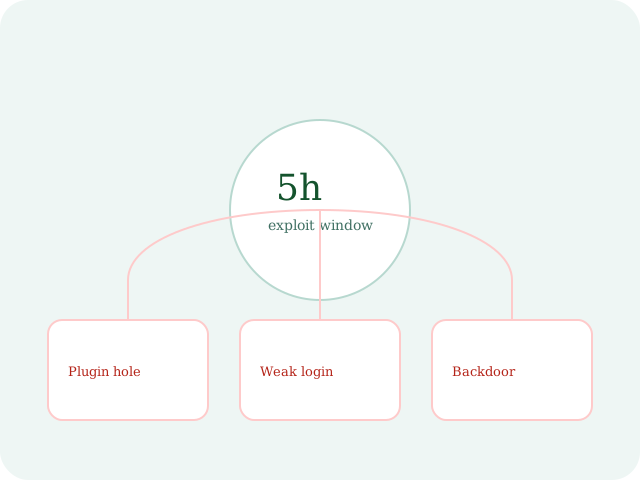
Automated scanners hit newly disclosed plugin holes in as little as five hours — faster than most sites click Update.
More than 90% of successful entries come from third-party plugins, weak logins, or leftover backdoors — not WordPress core.
Hacks inject SEO spam, skim payment forms, and get the domain blacklisted long before the homepage looks broken.
What we handle
Monitoring, firewall, cleanup, access, backups, and virtual patches — one desk, not three overlapping plugins.
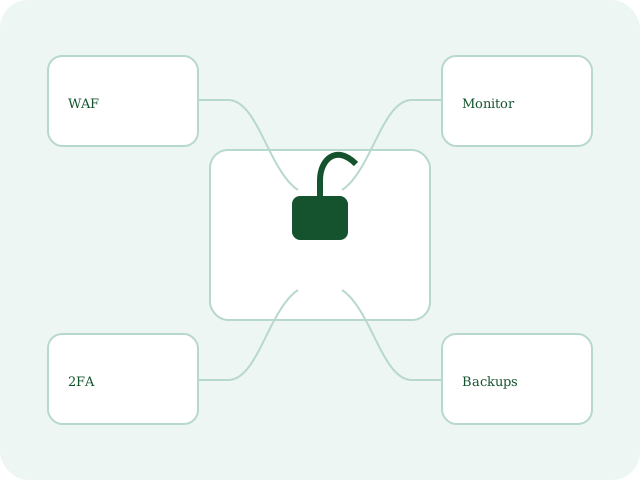
Unauthorized file changes, backdoors, and injected scripts are flagged as they land — not at the next weekly scan.
Rules aimed at SQL injection, XSS, and bot nets, tuned to your login path and checkout — not a generic cloud checkbox.
Emergency cleanup, backdoor removal, and Google or McAfee blacklist work with the catalog still intact.
Two-factor for administrators, a non-default login URL, and brute-force limits that do not lock out real staff.
Encrypted daily copies off the host, so a wipe or a bad plugin cannot take the only restore with it.
Known plugin holes are contained before the vendor ships an official update.
Choose the job
If the site is already owned, that is a cleanup. If it is still clean, that is a retainer. Do not buy the wrong one.
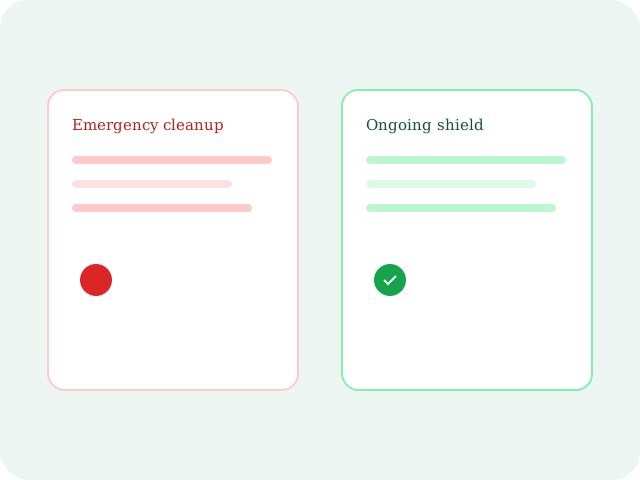
Option A · one-time
For sites that are hacked, redirected, or blacklisted.
Option B · monthly
For owners who cannot afford the next incident.
Process
Audit, harden, watch, then report. Live checkout stays up while the work is proven.
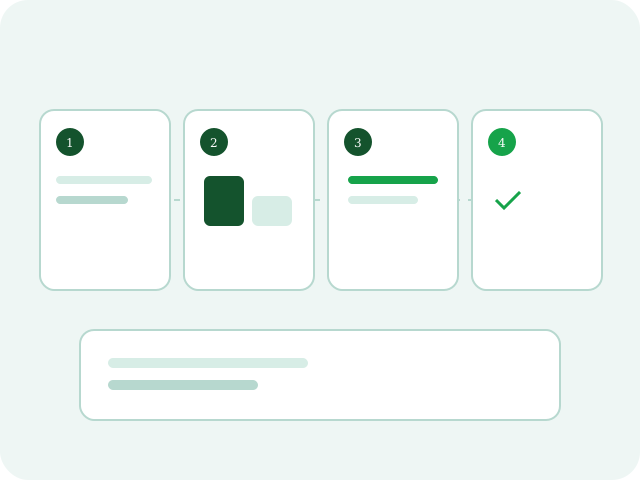
Core, database, themes, and the server are checked for holes and hidden backdoors.
File execution is restricted, database access is tightened, and the firewall goes live.
File integrity, SSL, and odd logins are watched in real time.
If something trips, we contain it and send a plain-language incident note.
Trust
We cleaned an infected WooCommerce store with 50,000+ monthly visitors and had search indexing back within 48 hours. Checkout card flows are treated as PCI-relevant work, not a plugin toggle.
The store was serving spam to Google. They had checkout clean and Search Console clear inside two days.
We finally stopped guessing whether the host “already covers it.” The WAF logs are readable.
Retainer meant the next plugin CVE was patched on staging before we read the email.
FAQ
Host firewalls catch a lot of server noise. They rarely stop application-level WordPress exploits: a vulnerable plugin, a weak admin password, or a leftover backdoor in uploads.
A tuned WAF and bot blocking usually free bandwidth. We do not stack three security plugins that scan the same files on every page load.
Cleanup is included. We isolate, restore or clean, and reopen search listings. There is no extra emergency invoice for retained sites.
Temporary admin and server access is required for the first hardening pass. Credentials go through an encrypted manager and are reduced once monitoring is live.
Customer data and checkout do not wait. Tell us if the site is already owned, or if you want the retainer before the next CVE.